Upgrade & Secure Your Future with DevOps, SRE, DevSecOps, MLOps!
We spend hours scrolling social media and waste money on things we forget, but won’t spend 30 minutes a day earning certifications that can change our lives.
Master in DevOps, SRE, DevSecOps & MLOps by DevOps School!
Learn from Guru Rajesh Kumar and double your salary in just one year.
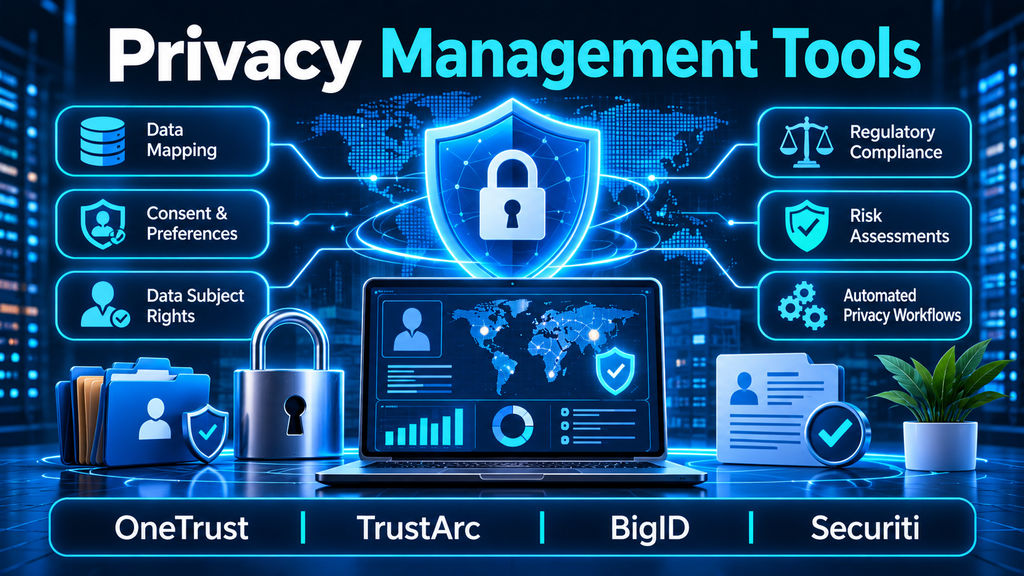
Privacy Management Tools: Building Trust Through Data Governance, Compliance, and Automation
Introduction
Personal data is now distributed across customer relationship management systems, cloud platforms, collaboration tools, mobile applications, analytics environments, outsourced services, and AI systems. This creates a difficult operational challenge: an organization may have policies explaining how personal information should be handled, yet still struggle to identify exactly where that information resides or whether every business unit follows the required controls.
Privacy management tools help close this gap. They provide a structured environment for documenting data processing, managing consent, responding to individual rights requests, assessing privacy risks, monitoring third parties, and maintaining evidence of compliance.
Their purpose extends beyond regulatory paperwork. A well-designed privacy program helps organizations make responsible use of data while reducing unnecessary collection, limiting exposure, and improving customer confidence.
What Are Privacy Management Tools?
Privacy management tools are software platforms that help organizations plan, operate, monitor, and demonstrate their privacy programs.
Depending on the product, capabilities may include:
- Data inventory and mapping: Documenting personal data, its sources, storage locations, purposes, recipients, and movement between systems.
- Records of processing activities (RoPA): Maintaining structured records of how personal data is processed.
- Consent and preference management: Capturing user choices and ensuring those choices are respected across relevant systems.
- Data subject request (DSR/DSAR) management: Coordinating access, correction, deletion, portability, and other rights requests.
- Privacy impact assessments: Evaluating the risks associated with new products, processing activities, vendors, and technologies.
- Third-party privacy management: Assessing service providers and tracking contractual privacy obligations.
- Incident and breach workflows: Coordinating privacy incident assessments, escalation, documentation, and response.
- Regulatory management: Mapping internal controls and processes to applicable privacy obligations.
- Reporting and audit evidence: Producing records that demonstrate how privacy activities are performed.
Not every platform provides all these capabilities at the same depth. Some products concentrate on consent and consumer rights, while others emphasize enterprise privacy operations, data discovery, or governance.
Why Organizations Need Privacy Management Software
1. Personal data is difficult to track
Information about one individual can appear in databases, email archives, support tickets, cloud storage, marketing systems, and external processors. Without a maintained inventory, privacy teams may not know which systems need to be included in a request or risk assessment.
2. Privacy requests involve multiple departments
A deletion or access request can require coordination among customer support, legal, IT, security, data owners, and application administrators. Email-based processes make it difficult to track deadlines, approvals, exceptions, and completion evidence.
3. Privacy obligations vary by jurisdiction
Organizations operating across regions may need to manage different rules for transparency, consent, retention, international transfers, and individual rights. A centralized platform can help maintain a consistent operating model while recording jurisdiction-specific requirements.
4. Vendor ecosystems expand the privacy boundary
Personal information may be processed by payment providers, analytics vendors, cloud platforms, marketing services, and business-process outsourcers. Privacy teams need visibility into these relationships and the controls expected from each provider.
5. Manual compliance does not scale
Spreadsheets and shared folders can support an early-stage program, but they become difficult to maintain as systems, business units, processing purposes, and regulatory obligations multiply.
Automation can reduce repetitive coordination. It does not replace legal interpretation, accountable decision-making, or verification that a control actually works.
Core Capabilities to Evaluate
Data inventory and processing maps
A useful privacy inventory should identify the personal data involved, the purpose of processing, the systems and business owners involved, retention expectations, recipients, and relevant safeguards.
The platform should make it possible to update records as applications, vendors, and processing activities change. A static inventory created for an audit can quickly become unreliable.
Consent and preference management
Consent management records choices and helps communicate those choices to downstream systems. Evaluation should include:
- Clear records of when and how consent was collected.
- Support for withdrawal and preference changes.
- Versioning of consent language and notices.
- Integration with websites, mobile applications, and relevant business systems.
- Evidence that downstream systems receive and honor preference changes.
- Configurable rules for different regions and processing purposes.
A consent banner alone is not a complete consent-management program. The organization must also understand how the recorded choice affects actual data collection and use.
Data subject request automation
A privacy platform can coordinate the request lifecycle:
- Receive and classify the request.
- Verify the requester’s identity using an appropriate process.
- Identify systems likely to hold the individual’s information.
- Route tasks to the relevant system and data owners.
- Review results for exemptions, legal holds, and other constraints.
- Complete the approved action.
- Record the response and supporting evidence.
Automation should not automatically delete every matching record. Legal retention duties, fraud investigations, contractual requirements, and other lawful exceptions may need review before action.
Privacy assessments and risk management
Privacy impact assessments help teams evaluate proposed processing before it becomes operational. Useful features include reusable questionnaires, risk scoring, approval workflows, mitigation tracking, and reassessment triggers.
The platform should connect assessment findings to accountable owners and remediation tasks. A completed questionnaire without follow-through offers limited risk reduction.
Third-party privacy management
Vendor assessments should capture the type of personal data shared, processing purpose, geographic location, subprocessors, security controls, contractual commitments, and deletion or return requirements.
Look for workflows that connect assessments to procurement, legal review, contract management, and ongoing vendor monitoring.
Regulatory intelligence and evidence
Organizations need to understand which obligations apply to particular activities and how internal controls address them. Regulatory libraries can help teams track changes, but applicability still requires knowledgeable review.
A strong evidence model should retain ownership, timestamps, approvals, policy versions, exceptions, and remediation history.
Leading Privacy Management Platforms
The following products illustrate different approaches to privacy operations. They are not a universal ranking: the best choice depends on the organization’s existing systems, privacy maturity, data architecture, and required workflows.
1. OneTrust Privacy Management
OneTrust offers a broad governance platform with privacy operations, data subject request automation, consent and preference management, and related governance capabilities.
It is worth evaluating when an organization wants to coordinate multiple privacy processes through a shared platform. Buyers should examine which modules are required, how workflows connect, and whether the licensing model fits the intended deployment.
Official product information: https://www.onetrust.com/products/
2. TrustArc
TrustArc provides privacy program management capabilities spanning governance, consent, individual rights, assessments, and regulatory compliance workflows.
Its approach can suit organizations that need structured privacy program development and ongoing compliance management. Buyers should validate how the platform represents their data flows and how easily business teams can maintain records over time.
Official product information: https://trustarc.com/products/
3. BigID Privacy and Compliance
BigID brings privacy automation together with data discovery and intelligence capabilities. Its privacy offering describes workflows for data rights, consent, records of processing, assessments, and data-related governance.
This approach may be useful when identifying personal data across complex data estates is a central requirement. During evaluation, test discovery accuracy across structured, unstructured, cloud, SaaS, and other relevant repositories.
Official product information: https://bigid.com/solutions/privacy-and-compliance/
4. Securiti Data Privacy
Securiti provides privacy and data governance capabilities that connect privacy workflows with an organization’s data environment. Its platform is relevant to buyers looking for discovery-led privacy operations and automation across distributed systems.
Evaluate connector coverage, identity resolution, workflow accuracy, deployment requirements, and the controls available for sensitive data.
Official website: https://securiti.ai/
Platform comparison
| Platform | General approach | Areas to evaluate | Potential fit |
|---|---|---|---|
| OneTrust | Broad privacy and governance platform | Privacy operations, DSR automation, consent, integrations | Organizations coordinating multiple governance workflows |
| TrustArc | Privacy program and compliance management | Assessments, individual rights, regulatory workflows | Teams formalizing or scaling privacy programs |
| BigID | Data discovery-led privacy and compliance | Data discovery, rights workflows, consent, governance | Organizations with complex and distributed data estates |
| Securiti | Data-centric privacy automation | Discovery, privacy workflows, integrations, governance | Enterprises seeking to connect privacy operations with data intelligence |
This comparison describes product positioning, not a guarantee that every capability is included in every edition. Confirm module availability, licensing, regional support, and integration details directly with each vendor.
How to Select the Right Privacy Management Tool
Start with the privacy operating model
Before reviewing software, document how privacy work is performed today. Identify who owns the data inventory, who handles rights requests, who approves assessments, and how vendors and incidents are managed.
The goal is to identify operational gaps rather than buy a large platform simply because it offers many modules.
Map the systems that matter
List the major repositories and applications that contain personal data. Include cloud services, SaaS applications, business databases, collaboration tools, customer platforms, and relevant third-party systems.
Ask vendors to demonstrate discovery and workflow coverage against representative systems from this inventory.
Prioritize integration quality
A platform may offer an impressive workflow interface but still require substantial manual work if it cannot connect to the systems where data is held.
Assess:
- Native connectors and supported versions.
- API coverage and rate limits.
- Authentication and access requirements.
- Handling of failed or incomplete integrations.
- Logging and evidence of actions performed.
- Support for custom applications and legacy systems.
Examine identity matching carefully
Data subject requests depend on finding the correct individual’s information. Matching only on an email address may miss records associated with alternate addresses, customer IDs, former names, or other identifiers.
Test matching accuracy and false positives with realistic scenarios. Confirm that human review is available before sensitive actions are taken.
Evaluate workflow flexibility
Privacy processes vary by organization, jurisdiction, and request type. Check whether the platform supports configurable routing, approvals, deadlines, escalation, exceptions, and evidence retention without extensive custom development.
Validate reporting and auditability
Reports should show more than a completion percentage. Look for traceable evidence of who performed an action, when it occurred, which systems were involved, what exceptions were applied, and who approved the result.
Understand total cost of ownership
Consider subscription costs, modules, implementation, integration development, data preparation, training, administration, and ongoing support. A platform with a lower entry price may require more services or custom engineering to meet enterprise requirements.
Common Implementation Challenges
Treating the platform as the source of truth before validating the data
Importing inaccurate inventories or outdated processing records can create a polished but unreliable privacy register. Establish ownership and validation procedures before treating imported records as authoritative.
Automating poorly defined processes
Automation can make a flawed process run faster. Define request categories, identity checks, exception handling, approvals, and escalation rules before building workflows.
Overlooking unstructured data
Personal information may exist in documents, messages, support tickets, file shares, and collaboration spaces. A program that only inventories structured databases can leave significant blind spots.
Failing to involve system owners
Privacy teams cannot independently verify every repository or processing purpose. Application owners and business stakeholders must participate in discovery, assessment, and remediation.
Confusing documentation with enforcement
A platform may record a retention policy without enforcing deletion in the underlying application. Verify that policies connect to operational controls, or clearly document where manual action remains necessary.
Ignoring international transfers and subprocessors
Data can move across borders through cloud hosting, support access, analytics, and vendor relationships. Maintain visibility into relevant transfer arrangements and subcontracting chains.
A Practical Deployment Roadmap
Phase 1: Establish scope
Identify applicable jurisdictions, business units, priority processing activities, major systems, and the teams responsible for privacy operations.
Phase 2: Build the inventory
Collect existing records, interview system owners, connect priority data sources, and validate the resulting data map. Record unknowns rather than treating incomplete information as confirmed.
Phase 3: Prioritize workflows
Start with high-volume or high-risk processes, such as data subject requests, consent management, privacy assessments, or vendor reviews. Avoid activating every module at once.
Phase 4: Integrate and test
Connect the relevant applications and test normal cases, exceptions, failed integrations, duplicate identities, and requests involving legal holds or retention requirements.
Phase 5: Train stakeholders
Train privacy teams, legal, security, IT, procurement, customer support, and business owners on their responsibilities and escalation paths.
Phase 6: Monitor effectiveness
Track operational measures such as request completion time, overdue tasks, unresolved data sources, assessment remediation, vendor review status, and integration failures. Use the results to improve the program.
Questions to Ask During a Vendor Demonstration
- Which systems can the platform discover or connect to natively?
- How are data maps created, validated, and kept current?
- How does the product match an individual across multiple identifiers?
- Can deletion workflows respect legal holds and retention exceptions?
- How are consent withdrawals propagated to downstream applications?
- Can workflows vary by jurisdiction, request type, and business unit?
- What evidence is retained for approvals and completed actions?
- How are failed integrations and incomplete searches surfaced?
- Which capabilities require separate modules or additional licensing?
- Can the organization export its records and workflow history if it changes providers?
A proof of concept should use representative systems and realistic privacy scenarios rather than relying only on a scripted demonstration.
The Role of AI in Privacy Management
AI can help classify data, suggest processing relationships, summarize assessments, identify potential risks, and accelerate the review of privacy records. It may also help teams understand how personal information is used in AI training datasets, prompts, outputs, and connected services.
However, AI-generated classifications and recommendations require validation. A model may misidentify sensitive information, overlook context, or suggest an action that conflicts with retention obligations.
Organizations should ask how AI features handle customer data, whether prompts and outputs are retained, how decisions are logged, and whether human approval is required for consequential actions. AI should improve the efficiency of privacy operations without weakening accountability.
Conclusion
Privacy management tools help organizations turn privacy commitments into repeatable business processes. By connecting data inventories, consent, individual rights, risk assessments, vendor oversight, and compliance evidence, these platforms can reduce manual coordination and improve visibility into how personal information is handled.
The most effective selection is not necessarily the platform with the longest feature list. It is the one that fits the organization’s data environment, integrates with the systems that matter, supports accountable workflows, and makes it possible to verify that privacy controls operate in practice.
A successful privacy program depends on more than software. Clear ownership, accurate data, sound legal interpretation, effective integrations, and continuous review remain essential. The platform provides the operational foundation; the organization must ensure that privacy principles are reflected in everyday decisions.
